100% Guaranteed!

The previous blog post about our websites being up 99%+ of the time leads to another discussion. We had a prospect who wanted to host with a different outfit. This group guaranteed 100% uptime. We can't guarantee that, so the prospect went with the 100% hosting provider. Why don't we use this '100% uptime' group?

Well, here's the truth: there is No Such Thing as 100% uptime. We was previously that no network is ever up 100% of the time. Network engineers design for '4-nines' uptime: 99.99% or maybe 'five-nines' 99.999% each extra '9' you tack on costs about a factor of 10 more than the previous '9'. Yes, there's several outfits that guarantee '100% uptime', but it's a hallow promise. Their networks really only deliver 99.99% uptime. So how can they guarantee 100%? Simple. They charge about three times as much as we do for hosting and their guarantee states that if your site ever goes down, you get that month's hosting for free. Their business model is to charge so much for hosting that when the inevitable glitch occurs, they have plenty of your money on hand to give you a free month's service. In other words, this is the hosting equivalent of an extended warranty. You pay an awful lot for the occasional service repair. I don't like these outfits because they know, as do I, that the '100%' promise is something they really can't fulfill, but they overcharge as much as they overpromise in order to give you a refund when it's called for. Something about this just rubs me the wrong way.

3by400 Hosting in Gartner Magic Quadrant 2015

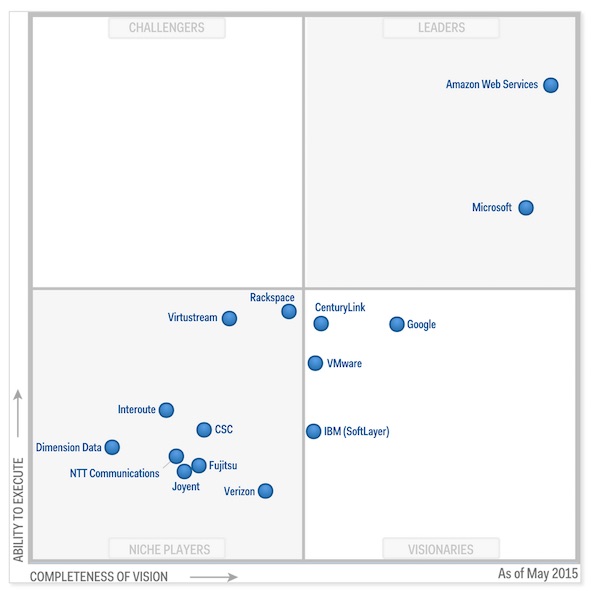
3by400-gartner-2015-mq-cloud-iassJust a quick note to celebrate the fact that your 3by400 hosting is based upon one of today's technology leaders, according to Gartner Group.

In the 2015 Magic Quadrant for Cloud Infrastructure as a Service, Worldwide, Gartner placed Amazon Web Services in the “Leaders” quadrant and rated AWS (Amazon Web Services) as having both the furthest completeness of vision and the highest ability to execute. See more about the report here, including the ability to download.

This news simply validates what we have come to understand in choosing it as the core of our most stable, reliable, and high-performing hosting platform. We literally sleep better at night after migrating to AWS in late 2013, and hope you do, too!
If you have questions about your current hosting service, or would like to transfer your Joomla site to 3by400 hosting, please contact us.

5 Ways I Keep My Family Safe on the Internet

These days, every device, every video game system—even THINGS (IoT)—access the internet. So, in a world where the internet is inescapable, how do we protect our children? How do we help them hold onto their innocence?

My husband and I have been increasingly focused on these questions as our children get older, become more independent, more tech savvy, and more inquisitive.
movie theater signWe have always run a “tight ship” in terms of closely monitoring the television shows we watch as a family, movies we see at the theater, or video games we play. Thanks to sites like Common Sense Media or the IMDB Parent’s Guide we are able to see a categorical breakdown of the media’s content in terms of subjects like profanity, violence, positive message, consumerism, and nudity. When it comes to our kids and the internet, however, there is no all-inclusive parent’s guide. Everything is at their little fingertips.

There was a time that we were naive enough to think that using Youtube Restricted Mode or Google Safe Search was an adequate method of keeping the “bad stuff” out. I’m here to tell you IT'S NOT, which we have, unfortunately, learned the hard way. Those site-specific methods are largely community monitored, meaning that a YouTube video is only flagged as “inappropriate” if a YouTube user marks it as such. Even the YouTube Kids App, whose target audience is children ages 3-8, includes a disclaimer that its possible for inappropriate content to slip through.

After my husband and I researched solutions, we ultimately determined that we needed a device capable of filtering and monitoring internet traffic as it entered our home, giving us the power to self-monitor and filter out the “bad stuff”. We have also taken full advantage of the built-in parental control features in our childrens' devices.

So, here is a breakdown of five (5) parental controls, in no particular order, that we have implemented in our home that are proving to be effective. I will followup with details about the specific hardware device we chose to purchase as a result of our own research. 

1. Time Restrictions
Setting limits in general is beneficial in a child's world—and in an adult's world too. The same holds true for internet usage. Establishing time limits and time restrictions for your family can help them stay safe on the internet, such as preventing late-night browsing that could put children in danger or encouraging internet in moderation by setting daily usage limits. We have put this into action in our home by using available technology to create unique profiles for each member of our family, then enforcing individual bedtimes by scheduling the internet to turn off at configured times. We also set individual internet usage limits per day and "Off times" during homework and family meal times.

2. Filtering
While we can't always trust websites and services to adequately filter out inappropriate content, we can take some control into our hands by filtering out content before it gets to our kids at the point of entry—the router or WiFi access point. Depending on the filtering hardware you choose, you may have broad filtering options to block content categorically, such as blocking all "Adult" content, although, in most cases it's best to have more granular control.

For example, blocking all websites categorized as "Videos" would block everything from YouTube to Netflix, to PBS Kids, but with finer control, you can choose the specific sites to which you want to allow or disallow access. We used our individual internet access profiles to set a combination of several categorical filters (eg. adult content and social media sites) and site-specific filters (eg. YouTube) based on the age and maturity level of the family member.      

3. Logging
Ideally, the software or device you choose will have logging capabilities. Internet history logs and usage logs are beneficial in several ways, including monitoring where your children are going on the internet, and whether the filters you've put into place are doing their jobs. We keep history logs and usage logs on each individual family member and device connected to our home network. From the logs, we can determine how much time each family member has spent online—total and per website visited—where they spent their time, and which browsing sessions were successful and which were denied access.   

4. Restricted Accounts

Most devices and services these days have some form of built-in parental controls out of the box, so its best to take full advantage of those tools already at your disposal. While the setup of the parental controls will vary from device to device and service to service, most have similar features: the ability to setup separate "parent" and "child" accounts; the ability to restrict those accounts to features of your choosing; and the ability to setup a password or PIN requirement in order to bypass the restrictions or gain access to the settings. We have setup each of our family's devices in this way.

Our children's Apple products are setup with Family Sharing and each person has a unique Apple ID. This allows us to control each Apple ID in terms of what services are allowed. I also receive a notification any time a 'child' device wants to download a new app, or access a restricted feature, with the ability to approve or dissaprove the action.

On our Android devices we've setup Restricted Profiles. Similar to the Apple devices, we can use the restricted profile to control which apps and features are allowed and also lock the ability to change those settings with a passcode.

In terms of services, we are fairly heavy users of Netflix. We have setup a Netflix account profile for each family member and assigned one of the available profile levels for each person based on their age and maturity level. This allows us to filter Netflix content based on rating. One well-documented drawback of Netflix is there is no way within the app to prevent profile switching, which pretty much makes profiles for the purpose of filtering out innapropriate content null and void. However, when Netflix is used on an android device with a restricted profile, the android software can prevent netflix profile switching. So, we're using those in tandem. Hopefully, Apple devices will add that feature in the near future.


5. Communicate and Educate
Last, but definitely not least, is to communicate with your children about the importance of internet safety and keep yourself educated. As parents, we can implement all the safeguards in the world in our homes to protect our children, but there will always be vulerabilities. They're going to get on the internet at friends houses or grandparents homes. They're going to push limits and find loopholes. They've grown up in a generation that has been immersed in technologies that weren't even thought to be a capability when we were their age. Seize the opportunity to have those important conversations and at an early age, but keep them age-appropriate.

Also, as parents we must stay educated on the latest technologies, including the newest innapropriate app or social media platforms. Technology is getting “smarter”, and parents must get smarter, too. I highly recommend NetSmartz.org, by the National Center for Missing & Exploited Childrenfor this purpose, a favorite resource for several presentations I have made to parents. They offer games, videos, training resources, and other tools for all ages, and they regularly update their resources to stay up-to-speed with the latest technologies. Their other sites, NetSmartzKids.org and NSTeens.org, will be of interest, too.  

Our Technology Choice
After much research, and learning from our mistakes, we decided to go with the Circle device. Circle was incredibly easy to setup—plug it in, connect to it via WiFi with a smartphone, provide it with the password to your WiFi access point, and voila! Unlike other solutions, there was no device-specific software installation or configuration.

From there, we setup each family member's profile, configured filtering levels and time limits, and then assigned their devices to their profile. Now, from the simplicity of an app, we can view logs, pause the internet for anyone or everyone, adjust filters, receive push notifications anytime a new device connects, or even send rewards to our children like late bedtime or extended usage.

We've been happy with the way Circle has worked for us so far, and for a brief period we feel like we've got a handle on this whole thing—until the next big advancement in technology comes along. I'm guessing we have about a week. Its a neverending learning and adjusting experience, but our children are worth it!
Backing Up on Square Wheels

One of the things we try hard to do is not reinvent the wheel. That's why we use Joomla! instead of writing our own Content Management System, why we search hard for off-the-shelf components before we write our own. For our servers, we rent from a large, reputable company and use one of the three industry-standard control panels. This is to give our customers the best value for their money by not reinventing wheels and for security, in case we lose a team member as standard skills are much easier to replace. There's one exception to our 'never reinvent the wheel' rule...

and that's of course if the wheel is square. Such was an ongoing struggle we've had: backup. The control panel software we use had automatic scheduled backup facilities: daily or weekly backups, what time, how many to keep, etc. And for a server with very few sites it was probably adequate. One of our servers has about 80 sites and many have e-commerce on them so they have to be backed up nightly. The backup routines started taking longer and longer, with backups overlapping each other and slowing the system down. I wrote a procedure to try to spread them out, but still they piled up and hurt performance. So I finally took a weekend and ripped out the standard backup procedure and replaced it with a more robust one. This new one can do both full backups (everything on the site) and incremental (just what's changed from the previous backup). This is a major win because if you'll think about it, most of the contents of your site don't change from one day to the next. Now instead of keeping three days' worth of full backups with the old software, we can now keep seven days' of backup with the new software because we're only doing one full backup, then a series of daily incrementals.


All in all, you probably don't care about the gory details of backup, but that's just one of the behind-the-scenes things we worry about and try very hard to get right. The bottom line is that instead of slogging down the server for six hours a night, backup now runs smoothly in two hours. As a result, a couple of our sites had perfect 100% uptime for a month. And that's something everyone understands and appreciates.

Choosing Good Passwords

Choosing a good password is always a problem. The essential tension is that a good password should be easy to remember, yet hard to guess. Most people err on one side or the other. Most people choose passwords that are too easy to guess, such as the name of their spouse or pet. Any word in the dictionary makes for a quick security breach. We have other vendors who send us passwords like 8#{aUv7. Yes, it's hard to guess, but also impossible to remember, guaranteeing that it'll have to be written down, copied, pasted, stored, and generally left laying about. Here's some hints of forming usable passwords:

  • Combine two or more words, like 'noneshallpass'
  • Some people convert their passwords into 'leet speak' by substituting zeros for ohs (o->0) and ones for ells (l->1). These are fairly easy to guess as well. The next step up would be to substitute threes for ees (e->3)
  • Even better, if you speak a few words of a foreign language, use them. Such as: 'verb0ten'

NIST standards call for users to change their passwords every 90 days. This is commonly accepted wisdom in the security community, but I remain dubious. I think one well-chosen, well-guarded password is better than a string of mediocre passwords that change so often the user has to write them down to remember which one they're using at the moment.


In closing, have funwith the idea.

Domain, DNS, and Business Email Basics: Who Owns What

Your website and email depend on a few separate services that often come from different companies. When something breaks, or when you switch providers, knowing who controls what saves a lot of stress.

The four pieces

  • Domain name (like yourbusiness.com): you rent it yearly from a domain registrar.
  • DNS (Domain Name System): the settings that tell the internet where your website and email live. DNS is often managed at your registrar, but it can be somewhere else, like your host or a DNS service.
  • Web hosting: the server where your website's files and database live.
  • Business email: the service that handles your This email address is being protected from spambots. You need JavaScript enabled to view it. mailbox. It's best kept separate from your web hosting.

These can all be with one company or with four different ones.

Why we keep email separate from web hosting

We keep email off our web servers for tighter security. If your website has a problem, or you change hosts, your email keeps working. A dedicated email service is also built to filter spam, block phishing, and keep your messages deliverable.

We recommend a dedicated service such as Google Workspace, Microsoft 365, or Proton Mail. Each works well for small businesses, so the right one depends on the tools your team already uses. We can take care of the setup for you, including the DNS records each service needs.

Why ownership matters

  • The domain should be registered in your business's name, with an email address you control. If a former employee, designer, or agency registered it in their name, getting it back can be hard.
  • Know your registrar login. Keep it in a password manager with two-factor authentication turned on.
  • Turn on auto-renew and keep the payment card current. An expired domain takes your website and email down, and someone else can register it.
  • Keep contact details current so renewal and security notices reach you.

What DNS records do

You don't need to edit DNS yourself, but it helps to know the common records:

  • A / AAAA records: point your domain to your web server.
  • CNAME records: point one name to another (often used for www).
  • MX records: tell the internet where to deliver your email.
  • TXT records: used for verification and email security, including SPF, DKIM, and DMARC, which help keep your email out of spam folders and stop others from faking your address.

DNS changes can take a while to spread across the internet, so plan changes ahead of time.

When you change providers

  • Moving your website usually means changing A records. Your email shouldn't be affected if MX records stay the same, but check before you change anything.
  • Moving email means changing MX and related TXT records. Plan the switch so no mail gets lost.
  • Moving your domain to another registrar is separate from moving hosting. You'll need to unlock it and get a transfer code.

Before any change, write down or export your current DNS records.

Quick checklist

  • [ ] Domain is in the business's name
  • [ ] You have the registrar login, with two-factor authentication
  • [ ] Auto-renew is on
  • [ ] You know where DNS is managed
  • [ ] You know who hosts your website and who handles your email
  • [ ] SPF, DKIM, and DMARC are set up for your email
  • [ ] Logins are stored somewhere the business controls, not one person's inbox

Related

How 3by400 can help

Whether we build your site or you move an existing one to us, we can host it with our boutique hosting, which includes all the usual hosting features plus tight security, nightly backups, and 24/7 outage monitoring. If you're moving your site to our boutique hosting, we handle the whole move, including DNS, so you don't have to change records yourself. That includes keeping your email records (MX, SPF, DKIM, and DMARC) pointed at your email service so mail keeps flowing. Email itself stays with your email provider, and we can set up Google Workspace, Microsoft 365, or Proton Mail if you need it. Start a project or move your site.

Start a project

Ready to talk about your website? Start a project or reach us at 678-379-9321 or This email address is being protected from spambots. You need JavaScript enabled to view it.. We're based in Dalton, GA, and work with businesses everywhere.

Domains Held Hostage

For some companies, web sites are a nicety—they exist as a brochure but don’t really drive business. Other companies depend upon their web sites for sales and new client generation to such a large degree that their livelihood is dependent upon their web site.

Over the past five years, I have helped rescue scores of domains for helpless consumers to whom the Internet and their web sites are somewhat of a mystery. I still receive frequent calls that range from “my domain is registered in the web design company’s name” to “the registrar says I have to pay $180 to transfer my domain.” Registration is the very foundation of your web site lifecycle, so it’s important to choose wisely. 

Much like me going to a dishonest auto mechanic, many customers can be easily tricked by unscrupulous web designers and feigned domain registrars, or simply left in trouble if a company in their link of site ownership becomes unstable. This article should help you make sure that your company’s web site is not in jeopardy of being held hostage.

gi_domains

Hosting Is Not Domain Registration
Many consumers make the mistake of only searching tools like www.findmyhost.com to locate and engage a domain registrar. This site and others like it relate to hosting your site and do not specialize in domain registration.

Hosting service is the provision of storage space (like your hard drive) on the Internet. It is the second layer of launching a web site, built upon the foundation of domain registration. So, registration and hosting are two separate functions—don’t get them confused. For the most part, hosting companies are middlemen. The problem with using a middleman—a third party that performs bulk registrations through an official registrar—is that accounts are generally set up in the third party’s name, giving you no direct access to your domain record. These firms use accredited ICANN registrars to process your order, but do so behind a closed curtain so the transaction is hidden from you. The hosting company has generally become an affiliate to the registrar, meaning that they get some type of reward for setting your domain up with that registrar. I’m not saying affiliate programs are wrong, but the reward structure can sometimes motivate hosting companies to choose the wrong registrar.

Use Legitimate Domain Registrars
Not every company offering $5.00/year domain registration is an official ICANN registrar. ICANN (Internet Corporation for Assigned Names and Numbers) is a non-profit, public interest group that oversees the global domain name service. In ICANN’s own words, it is “responsible for managing and coordinating the Domain Name System (DNS) to ensure that every address is unique and that all users of the Internet can find all valid addresses. It does this by overseeing the distribution of unique IP addresses and domain names. It also ensures that each domain name maps to the correct IP address.

“ICANN is also responsible for accrediting the domain name registrars. ‘Accredit’ means to identify and set minimum standards for the performance of registration functions, to recognize persons or entities meeting those standards, and to enter into an accreditation agreement that sets forth the rules and procedures applicable to the provision of Registrar Services.”* Say what?

Basically, they are the ones who make sure that companies are playing by the rules in terms of making the Internet continue to work as we expect. They also make sure that TCP/IP (the protocol of the Internet) addresses are not duplicated.

ICANN is the place to which end users can present claims of misbehavior for those registrars who have official ICANN accreditation. Business news is fraught with accounts of misbehavior, such as requiring additional, undocumented funds for transfers or disallowing the modification of the domain record.

Before you or your consultant registers a domain, go to www.internic.net/origin.html to see a list of accredited registrars by country. It is a good idea to register in the country in which your business is located. You should also perform some Internet research to find out any existing user claims against your selected registrar, but do so with caution. Some end users “flame” a vendor when they themselves may be using a wrong approach.

When you are evaluating domain registrars, be sure to choose one that provides full contact information (including a phone number) and a documented escalation procedure. About half the time you need support from your domain registrar, it will be an emergency situation. You don’t want that to be the time to figure out that there is a 24-hour response time on support requests or that their support is only available between the hours of 10:00am and 4:00pm PST. Know before you buy.

We use GoDaddy.com, which has been flamed by many past users. Our experience is that over the last 5 years, they have proven a reliable, fully compliant, accredited registrar with excellent support and business practices. Additionally, they maintain a reasonable price structure for domain registration and a great tool for managing multiple domains. And, no, my company is not an affiliate!

Own Your Domain
One of the perils of “knowing enough to be dangerous” is that it may appear that your domain is registered to you when it is actually registered to your hosting company or the web design company you’ve hired. To promote the concept of domain ownership with our clients, we typically walk them through the process of purchasing their domain name. We take the opportunity to answer questions and make sure the tremendous amount of up sell information does not mask legitimate registration options.

A credit card must be used with most registrars and it is important for you to use your own credit card so you know when and what charges are made in relation to domain registration. Once the process is completed, you will be sent an e-mail receipt and confirmation of the registration information, including your account name, so it’s important that your e-mail address is documented in the registrant section. These are important documents that should be retained as permanent records. Be sure to include the password you selected for your account as well.

No matter how busy you are, knowing that you own your domain is one of the most important steps to launching a successful site and maintaining control over what might be one of your most valuable assets. You should have a URL, a username, and a password that allows you to make any necessary changes to your own domain. You may leave this to your trusted consultant, but you should always know that you have access to this information…just in case. If you maintain control of this information, you will significantly reduce the possibility of being held hostage. 

To check ownership of your site, go to www.whois.com and enter your domain name. Even if the site is privately listed (so ownership information is hidden), the registrar of the site should be listed. Alternately, if you go to www.godaddy.com, type your domain name in the domain search, then click the “more info” button.

Stay Flexible
There is a delicate balance between registering your domain for permanence and flexibility. Unless you know that a domain will not remain a permanent asset, always register for at least two years. The best registrar today may not be the best registrar tomorrow, such as was the case with RegisterFly.com.Your ICANN-accredited registrar will notify you when your domain is about to expire, so you have the opportunity to evaluate if they were the right choice for you. If so, re-up for two more years. If not, go to your newly selected registrar and start the domain transfer process. 

How Do I Ransom My Domain?
If you are in a situation where a hosting company or a past consultant has left you powerless over your domain, you should start with finding out where the site is registered (see above “who is” steps). Contact the registrar to find out what their specific process is for reclaiming your domain. For many registrars, the process consists of proving that you are a legitimate agent of the company represented on the site—yet another good reason to make sure your site is truly representative of your company. You may not feel comfortable faxing a copy of your driver’s license on official company letterhead to the registrar, but that may be what it takes. Whatever you are asked to send, make sure you know exactly why the registrar requires that information. If other sensitive information on that document is not required, mark it out. Don’t allow a bad situation to turn worse by exposing personal information unnecessarily.Make sure that the registrar changes the registrant e-mail address listed for the domain to match your current address. Sometimes, doing this is all that’s necessary for them to send a password reset that allows you access to your site. 

If you decide to transfer your domain to another registrar, make sure that you retain the DNS settings so the hosted portion of your web site is not lost. Another bad-to-worse situation is saving your ransomed domain name only to lose the content of your web site.

If your domain is currently being held hostage, hopefully, these steps will help you free it and become master of your domain. Otherwise, be sure to find a reliable, trustworthy professional who can help you on a web rescue.


*From www.icann.org/faq/

This article used with permission from 400 Edition, Inc. It is unlawful to use this article or any portion of it without the expressed permission of its author. This email address is being protected from spambots. You need JavaScript enabled to view it.

Dot Con Artists

Several months ago, I wrote an article with information from the FTC about SPAM regulations. Since then, I’ve found their web site to be a treasure trove of information about Internet fraud. As problematic as SPAM and Internet cons are, it’s comforting to know that the Consumer Sentinel, a consumer fraud database, tracks the cons and the con artists. According to the FTC, here’s what online consumers are complaining about most:


gi_internet

Internet Auctions
The Bait: Shop in a “virtual marketplace” that offers a huge selection of products at great deals.
The Catch: After sending their money, consumers say they’ve received an item that is less valuable than promised, or, worse yet, received nothing at all.
The Safety Net: When bidding through an Internet auction, particularly for a valuable item, check out the seller and insist on paying with a credit card or using an escrow service.


Internet Access Services

The Bait: Free money, simply for cashing a check.
The Catch: Consumers say they’ve been “trapped” into long-term contracts for Internet access or another web service, with big penalties for cancellation or early termination.
The Safety Net: If a check arrives at your home or business, read both sides carefully and look inside the envelope to find the conditions you’re agreeing to if you cash the check. Read your phone bill carefully for unexpected or unauthorized charges.

Credit Card Fraud
The Bait: Surf the Internet and view adult images online for free, just for sharing your credit card number to prove you’re over 18.
The Catch: Consumers say that fraudulent promoters have used their credit card numbers to run up charges on their cards.
The Safety Net: Share credit card information only when buying from a company you trust. Dispute unauthorized charges on your credit card bill by complaining to the bank that issued the card. Federal law limits your liability to $50 in charges if your card is misused.

International Modem Dialing
The Bait: Get free access to adult material and pornography by downloading a “viewer” or “dialer” computer program.
The Catch: Consumers complained about exorbitant long-distance charges on their phone bill. Through the program, their modem is disconnected, then reconnected to the Internet through an international long-distance number.
The Safety Net: Don’t download any program to access a so-called “free” service without reading all the disclosures carefully for cost information. Just as importantly, read your phone bill carefully and challenge any charges you didn’t authorize or don’t understand.

Web Cramming

The Bait: Get a free custom-designed website for a 30-day trial period, with no obligation to continue.
The Catch: Consumers say they’ve been charged on their telephone bills or received a separate invoice, even if they never accepted the offer or agreed to continue the service after the trial period.
The Safety Net: Review your telephone bills and challenge any charges you don’t recognize.

Multilevel Marketing Plans/Pyramids
The Bait: Make money through the products and services you sell as well as those sold by the people you recruit into the program.
The Catch: Consumers say that they’ve bought into plans and programs, but their customers are other distributors, not the general public. Some multi-level marketing programs are actually illegal pyramid schemes. When products or services are sold only to distributors like yourself, there’s no way to make money.
The Safety Net: Avoid plans that require you to recruit distributors, buy expensive inventory, or commit to a minimum sales volume.

Travel and Vacation

The Bait: Get a luxurious trip with lots of “extras” at a bargain-basement price.
The Catch: Consumers say some companies deliver lower-quality accommodations and services than they’ve advertised, or no trip at all. Others have been hit with hidden charges or additional requirements after they’ve paid.
The Safety Net: Get references on any travel company you’re planning to do business with. Then, get details of the trip in writing, including the cancellation policy, before signing on.

Business Opportunities

The Bait: Be your own boss and earn big bucks.
The Catch: Taken in by promises about potential earnings, many consumers have invested in a “biz op” that turned out to be a “biz flop.” There was no evidence to back up the earnings claims.
The Safety Net: Talk to other people who started businesses through the same company, get all the promises in writing, and study the proposed contract carefully before signing. Get an attorney or an accountant to take a look at it, too.

Investments
The Bait: Make an initial investment in a day trading system or service and you’ll quickly realize huge returns.
The Catch: Big profits always mean big risk. Consumers have lost money to programs that claim to be able to predict the market with 100 percent accuracy.
The Safety Net: Check out the promoter with state and federal securities and commodities regulators, and talk to other people who invested through the program to find out what level of risk you’re assuming.

Health Care Products/Services
The Bait: Items not sold through traditional suppliers are “proven” to cure serious and even fatal health problems.
The Catch: Claims for “miracle” products and treatments convince consumers that their health problems can be cured. But people with serious illnesses who put their hopes in these offers might delay getting the health care they need.
The Safety Net: Consult a health care professional before buying any “cure-all” that claims to treat a wide range of ailments or offers quick cures and easy solutions to serious illnesses.
Can you avoid getting caught by a scam artist working the web? Not always. But prudence pays. The FTC offers these tips to help you avoid getting caught by an offer that just may not click:

  • Be wary of extravagant claims about performance or earnings potential. Get all promises in writing and review them carefully before making a payment or signing a contract.
  • Read the fine print and all relevant links. Fraudulent promoters sometimes bury the disclosures they’re not anxious to share by putting them in teeny-tiny type or in a place where you’re unlikely see them.
  • Look for a privacy policy. If you don’t see one—or if you can’t understand it—consider taking your business elsewhere.
  • Be skeptical of any company that doesn’t clearly state its name, street address, and telephone number. Check it out with the local Better Business Bureau, consumer protection office, or state Attorney General.

The FTC works for the consumer to prevent fraudulent, deceptive, and unfair business practices in the marketplace and to provide information to help consumers spot, stop, and avoid them. To file a complaint or to get free information on consumer issues, visit www.ftc.gov or call toll-free, 1-877-FTC-HELP (1-877-382-4357). The FTC enters Internet, telemarketing, identity theft, and other fraud-related complaints into Consumer Sentinel (www.consumer.gov/sentinel), a secure online database available to hundreds of civil and criminal law enforcement agencies in the U.S. and abroad. From www.ftc.gov/bcp/conline/pubs/online/dotcons.shtm.

This article used with permission from 400 Edition, Inc. It is unlawful to use this article or any portion of it without the expressed permission of its author. This email address is being protected from spambots. You need JavaScript enabled to view it.

E-mail Marketing Tips

If you utilize e-mail marketing to prospective customers, make sure you don’t become an offensive spammer. There are a few simple rules to follow that can make a difference between happy customers and angry spam recipients. These rules are outlined in the Federal Trade Commission’s (FTC) CAN SPAM Act, which went into effect January 1, 2004. The CAN SPAM Act applies to commercial and pornographic electronic messaging and carries penalties for non-compliance of up to $11,000. Learn more about the CAN SPAM Act at www.ftc.gov/spam, including how to turn in offenders.

Be legitimate. Masking header information (such as the sender and recipient’s actual e-mail addresses) is illegal. It makes sense. If the claims within the e-mail are honest, knowing who sent it is reasonable. 

Honesty is the best policy. Subject lines must reflect the content of the message. Baiting a reader with a subject line that is not indicative of the actual content sent within the body of the message is not an honest approach.

Provide a legitimate opt-out. Opt-out is a simple mechanism that allows a recipient to remove themselves from your list. This is generally a clickable link that allows the recipient to complete a form and results in their address being removed from your e-mail list. Opt-outs should be immediately honored.

Provide a valid postal address and notification of solicitation. The FTC also requires that the e-mail sender’s postal address be included within the body of the e-mail and that it be identified as a solicitation.

If you are about to start an e-mail marketing campaign, try using a product like Constant Contact to get you started. This package takes legal issues into account and helps you manage responses such as bounced (erroneous addressee) messages and opt-out.

Put these items into action to reduce the impact of spam on your life and ensure that you are playing by the rules. And if you receive a message that looks intriguing, do your research and don’t be scammed by the spammers!

About.com Offers some pretty decent tips about e-mail campaigns:

Address Recipients with Their Name in Email Campaigns
Make your newsletter recipients feel more like themselves, less like mere numbers by greeting them individually and personally.

Avoid $$$ Signs in Email Marketing Campaigns
Why "$$$" won't bring you $$$.

Avoid Email Marketing During the Holidays
Holidays are often holidays from email, too. That's why email marketing during the holidays is often not very effective.

Create a Clear Call to Action in Email Marketing Campaigns
Make sure recipients of your email marketing message know what you expect them to do (and what they can expect in return).

Don't Forget the Preview Pane in Your Campaign
Move the boring stuff down the page, and greet recipients with your best offer instead.

Email Marketing Needs to Reflect Your Corporate Design
If it's your email marketing, make people see instantly that it is your email marketing.

Emphasize with Words, Not Exclamation Marks in Your Copy
The path to successful email marketing is not paved with exclamation marks.

Experiment with Link Placement in Newsletters
Maximize performance by putting the right links in the right places.

HTML or Plain Text: Let Your Recipients Decide
If you can't decide whether you should publish your newsletter as HTML or plain text, do both and let your recipients decide individually which they prefer.

Include an Easy to Use Unsubscription Link in Newsletters
Unhappy subscribers are worse than no subscribers. An easy and fail-safe way to unsubscribe is a way to make subscribers happy.

Inform Your ISP About Your Email Marketing Activities
The connection to your ISP is one of the most important. So make sure they know that you're sending legitimate bulk email and won't disconnect you as a spammer.

Instruments of Email Marketing
There is more to email marketing than personalized mass mails and newsletters. Discover all the forms and instruments of effective email marketing.

Learn from Spam
Spammers can teach you a lot about email marketing.

Make it Easy for Subscribers to Change Their Email Address
Lose one address, gain another, retain a subscriber when a user's email address changes.

Make Sure Unusbscriptions are Effective Immediately
Avoid a spam-like impression by making sure unsubscriptions from your newsletters or email marketing lists go into effect immediately.

Newsletter Content Ideas: Asking the User's Questions
Content ideas usually have this form: "How can I do this?". So how can I get great content ideas?

Newsletter Content Ideas: Press Summary
Consolidating news provides a useful service to your newsletter subscribers, and it shows your expertise in the field, too.

Put Newsletter Sign-up Boxes on Every Page
Make sure visitors can sign up to your newsletter when and where they want.

Reply to Requests Within 1 Day
You've got 24 hours to win — or lose — a customer, so be sure to reply to emails within a day.

Rule of Thumb How Often to Send Your Newsletter
Find the right frequency for your email marketing efforts.

Rule of Thumb When to Send Your Newsletter
Monday, Tuesday, Wednesday, Thursday, Friday, Saturday or Sunday? Which day will work best?

Sales Pitch Makes No Newsletter
Newsletter subscribers expect and deserve content, which salespeak alone is not.

Use Your Name in the From: Line
People don't like to read mail from strangers or robots. But messages From: a name they know and trust are welcome. 

This article used with permission from 400 Edition, Inc. It is unlawful to use this article or any portion of it without the expressed permission of its author. This email address is being protected from spambots. You need JavaScript enabled to view it.

Got Spam?

I find that spam—not the spiced ham in a can variant, but the deluge of unsolicited commercial e-mail—has become the topic of many of my conversations of late. It’s always evident when a new spamming tool becomes available that has been cleverly developed to foil even the best spam filters on the market. In fact, one of my clients estimates that 90% of the e-mails he receives fall into the category of spam, and I believe him.


As much as my company tries to stay on top of efficient filters, e-mail cleansing tools, and effective mailbox rules, I still receive “hot stock tips” and new opportunities to earn a million dollars by facilitating an offshore financial transaction. Yeah, right—does anyone actually fall for those? Spam is frustrating on many levels: it’s time-consuming and costly to try to prevent; it can bury legitimate e-mails or even cause them to be lost, which translates to lost business opportunity; and it ties up valuable resources across the planet.


gi_gotspam

Why does spam exist?

Like many things, the concept of spam started from a legitimate beginning—using e-mail to market a company, product, or service. Compared to other marketing strategies, e-mail blasts are cheap and effective. No stamp required, no print or broadcasting ad to develop and purchase, and immediate notification of receipt/response. From a marketer’s standpoint, it just doesn’t get any better than that! It’s the “unsolicited” portion of the definition that makes spam problematic.


From a legal standpoint, spam falls into the category of free speech, and I, for one, am not willing for spam to be eliminated at the risk of my e-mails being censored or scrutinized by anyone other than the addressee. Of course, I’m not an abuser of my privilege of using e-mail to communicate with my customers and potential customers.


E-mail addresses are cheap (if not free) and are readily available. I’m always conscientious about giving out my e-mail address, but doing business in an electronic world means that it’s necessary to make it available for the world to see, even the spammers. It is unfortunate that the bad guys out there crawl web sites to harvest e-mail addresses, because not listing those addresses on your web site may hamper your ability to generate business. A safe workaround is to use web-based forms for client communication that are routed to appropriate e-mail addresses.


There are thousands of sources for e-mail lists, so spam enablers are making money by accumulating lists of our e-mail addresses for sale. List providers are yet another example of a good idea gone bad. Who wouldn’t want a list of their potential customers, especially if your business has a very targeted market? I have one client whose market has a personal net worth of $10 million. That list was $3,600 and worth every penny to my client.


The biggest reason that spam exists, though, is because, yes, people do fall for those unbelievable scams—they do give their credit card numbers to fly-by-night web sites for a $25 Rolex, and they try to buy Viagra from unscrupulous sources. Spam exists because the spammers make money and there is no real investment required.


How do I eliminate spam?

Reducing spam in your e-mail account is similar to growing roses, in that both situations require ongoing care. Much like fertile soil, ample sunlight, and water, using a combination of server-based filtering, third-party desktop add-ons, and e-mail application rules is the most effective strategy.


Like choosing good soil for a new rose bush, it is best to start spam prevention from your mail server. Depending upon your level of access to the mail server used for your account, you can generally enable filtering based upon specific criteria: the sender address or domain name (known as blacklisting); certain words in the subject; or words in the body of the e-mail. Some filters allow you to choose a degree of potential for spam, generally from 1 to 10, depending upon things like your address as a specific recipient (rather than a long list of recipients); a large number of links or images within the body of the e-mail; or the existence of common spamming phrases. The good thing about using server-level filters is that you will never see the offensive e-mails. The bad thing about server-level filters is that you may lose some legitimate e-mails in the process. When aiming for the happy medium, it’s best to err on the side of caution. Some server-based filtering simply applies a flag to suspect e-mail messages, which then have to be handled by your desktop-based e-mail application to delete or place in a separate e-mail folder.


Another note about server-based spam protection: Earthlink offers a tool that I term “by invitation only.” With this strategy, the sender has to go to a website and request to be put on the recipient’s list of acceptable senders. Although this will no doubt reduce or even eliminate spam, not every legitimate sender will go through this process. If you use this filter, it is best to manage the entries yourself, and not expect everyone who may send you e-mail to do so.


Second in the plan of attack against spam is the use of desktop utilities. These come in many forms—some virus-protection packages supply anti-spam features. One of my associates uses a package called Mail Washer, which offers a low-end version for free. To find the best application for your uses, take a look at this review site, which evaluates some of the top spam blocker packages available. Again, it is important to note that these packages are not an “install and never receive spam again” solution. The filtering will only be as good as the effort you put into the configuration of e-mail message handling and you will still have to go through the spam folder that is created in your e-mail package in order to make sure you don’t lose messages you need.


Closest to home, your e-mail package can also offer protection against spam. The Microsoft mail packages, Outlook and Outlook Express, both offer the creation of rules to handle messages. They work in a fashion similar to the server-based filtering described above, then carry out whatever action you deem appropriate. Messages can be checked for specific phrases in the e-mail subject or body, then deleted or placed into a specific folder for further verification. Microsoft provides some templates for message rules and even offers a fairly automated “block sender” list. Don’t expect significant success with blocking particular senders when it comes to mass spamming. Most spammers utilize free account providers, like HotMail, to mask their identity, so the message you just received from them will probably be the only one you receive from that particular e-mail account.


Speaking of accounts, if you decide that you will, once and for all, free yourself of spam, be certain to create a whitelist, which is a list of e-mail senders whom you trust. The whitelist is simply of listing of accounts whose messages you do not wish to go through the gamut of filtering that will hopefully eliminate the real spam. Most whitelists allow you to enter a domain name so that any specific account, as long as it comes from the whitelisted domain will be properly delivered.


Am I a Spammer?

If you utilize e-mail marketing to prospective customers, make sure you don’t become an offensive spammer. There are a few simple rules to follow that can make a difference between happy customers and angry spam recipients. These rules are outlined in the Federal Trade Commission’s (FTC) CAN SPAM Act, which went into effect January 1, 2004. The CAN SPAM Act applies to commercial and pornographic electronic messaging and carries penalties for non-compliance of up to $11,000. Learn more about the CAN SPAM Act at www.ftc.gov/spam, including how to turn in offenders.


  • Be legitimate. Masking header information (such as the sender and recipient’s actual e-mail addresses) is illegal. It makes sense. If the claims within the e-mail are honest, knowing who sent it is reasonable.
  • Honesty is the best policy. Subject lines must reflect the content of the message. Baiting a reader with a subject line that is not indicative of the actual content sent within the body of the message is not an honest approach.
  • Provide a legitimate opt-out. Opt-out is a simple mechanism that allows a recipient to remove themselves from your list. This is generally a clickable link that allows the recipient to complete a form and results in their address being removed from your e-mail list. Opt-outs should be immediately honored.
  • Provide a valid postal address and notification of solicitation. The FTC also requires that the e-mail sender’s postal address be included within the body of the e-mail and that it be identified as a solicitation.


If you are about to start an e-mail marketing campaign, try using a product like Constant Contact to get you started. This package takes legal issues into account and helps you manage responses such as bounced (erroneous addressee) messages and opt-out.


Put these items into action to reduce the impact of spam on your life and ensure that you are playing by the rules. And if you receive a message that looks intriguing, do your research and don’t be scammed by the spammers!


This article used with permission from 400 Edition, Inc. It is unlawful to use this article or any portion of it without the expressed permission of its author. This email address is being protected from spambots. You need JavaScript enabled to view it.

Hosting for your Joomla site

A prospective customer wrote us that he was offered a 'screeming deal' on GoDaddy for $7 per month. Would we still be able to support his site there? Here's what I wrote back...


If you choose to host your site at GoDaddy, we'll be of very limited help to you. They really don't do a good job of Joomla hosting, see: http://www.joomlahostingreviews.com/ where GoDaddy ranks near the bottom of the heap.

Also they're notorious for security breaches. See such tales of woe as: http://smackdown.blogsblogsblogs.com/2010/05/13/hosting-with-godaddy-might-want-to-rethink-that-decision/. You can google for literally thousands of others.

In short, they don't have the tools or apparently the inclination to really do a good job of hosting dynamic websites like Joomla or
Wordpress.

Also consider: would you really be saving money? As an example, this week a security patch for Joomla came out: 1.5.21. I installed it on all our sites automatically with no charge to our customers. If you were to be hosted at GoDaddy, I'd have to do a special one-of update for your site that would take me about a half hour. With my billing rate, you've just lost a number of months of savings that 'screaming deal' bought you.

It's your choice, but if you do go with GoDaddy, we'll not be able to offer the level of support we like to provide and that we think you and your site deserve.


That's where I ended the letter, so I didn't even get into such things as site performance enhancements we provide by tweeking the Apache webserver configurations, regular database integrity monitoring, backing Joomla sites up the right way (both files and database at the same time), intelligent database, joomla and php caching, etc. The long and short of it is: not all hosting providers are created equal and not many really understand how to host Joomla.


Hosting Issues

We try to host most of our clients' websites. We started doing this because we tried using a service that claimed to offer 'custom Joomla hosting' packages. After two days on that service and horrible website load times, the service called us and asked us to move the site off of their server, because it was getting too many visitors for their server to keep up with. We seem to be talking to more people these days who are using diverse hosting providers. Here's some of the issues we're running into with them:

  • Email bundling problems. Their hosting provider also provides email. We suggest moving to Google apps for their domain so they can have calendars, sites, really nice email, etc. But the hosting provider won't split up their hosting from email.
  • DNS problems. The hosting provider expects all the hosting to be on their machines. When we ask to set up a build site, like build.theirdomain.com that lives on our server, they balk.
  • Backup. One would expect this to happen by default, but not so. We recently investigated one ecommerce site that as near as we could tell, had NO backups. We finally got backups running, but the backups filled up the client's disk quota and the client could no longer get email. The very idea of backing up a site to the same disk where the site lives really isn't a backup as far as I'm concerned.
  • Old Joomla versions. Whenever a new Joomla version comes out, we run an automatic script to update all our sites. Sites hosted at other generic hosting providers generally are a number of revision levels behind. Why is this important? Because all the recent Joomla patches have corrected security holes. Running an older version of Joomla exposes your site to hackers.

The moral of the story? I guess one gets what one pays for with cheap hosting.

How to Add Users and Set Roles in WordPress

Using Joomla instead? See How to Add Users and Set Permissions in Joomla.

Giving each person their own login, with only the access they need, keeps your site safer and makes it easier to see who changed what.

WordPress roles

WordPress has five standard roles on a single site:

  • Administrator: full control, including plugins, themes, settings, and users. Keep this to as few people as possible.
  • Editor: can publish and manage all posts and pages, including other people's.
  • Author: can write, publish, and manage their own posts.
  • Contributor: can write their own posts but can't publish them.
  • Subscriber: can only manage their own profile.

(Multisite networks also have a Super Admin.) Plugins such as stores or membership tools may add their own roles.

Add a user

  1. Log in at yoursite.com/wp-admin.
  2. Go to Users > Add New User (labeled Add New in some versions).
  3. Enter a Username, Email, and optionally first and last name.
  4. Leave Send User Notification ticked so they get an email to set their password.
  5. Choose a Role.
  6. Click Add New User.

Change someone's role

  • Open Users > All Users, click the person's username, change Role, and click Update User.
  • Or tick several users and use Change role to above the list, then click Change.

Remove former staff

Do this as soon as someone leaves.

  1. In Users > All Users, hover over the user and click Delete.
  2. WordPress asks what to do with their content. Choose Attribute all content to and pick another user so their posts and pages stay on the site.
  3. Click Confirm Deletion.

If you'd rather not delete them yet, change their role to Subscriber and reset their password. Also change any shared passwords they knew, like hosting or FTP.

Two-factor authentication

WordPress doesn't include two-factor authentication. Your security plugin may add it. Turn it on for anyone with Administrator or Editor access.

Review users regularly

A few times a year, go through Users > All Users and remove accounts that aren't needed.

Related

Prefer we handle it?

If you'd rather spend your time running your business, our boutique hosting, available to our clients, including sites moved over from another host, takes a proactive approach to security and monitoring, with nightly backups, 24/7 outage monitoring, and ongoing core CMS updates.

How to Get Support From 3by400

Our support goes through our ticket system, so every request is tracked and nothing gets lost in an inbox. Here's how it works.

1. Sign in

Go to our support page and sign in under Returning User with the login we set up for you.

No login yet? Client accounts are set up by our team. Email This email address is being protected from spambots. You need JavaScript enabled to view it. and we'll send you one.

Forgot your password or username? Use Forgot your password? or Forgot your username? on the sign-in page.

2. Open a ticket

  1. Choose Open New Ticket, or go straight to the new ticket form.
  2. Pick what you need help with:
    • Site Enhancement: new features, pages, or changes to your site
    • Site Access: logins, passwords, admin or FTP access
    • Site Error: something broken, slow, or not working
    • Email issue / addition: email delivery problems or a new mailbox
    • General Question: anything that does not fit the other options
  3. Add a short subject, like "Checkout button does nothing on mobile."
  4. Choose a priority. Pick Critical only if the site is down or payments are failing.
  5. Describe the problem or change, attach screenshots, and submit.

You'll get an email with your ticket reference.

What to include

Help us help you faster:

  • The page address where it happens
  • What you expected, and what happened instead
  • A screenshot, plus your browser or device
  • One issue per ticket, so nothing gets missed

3. Track the reply

We reply within 1 business day, in the ticket and by email. You can see all your requests under My tickets on the support tickets page.

What the statuses mean:

  • Open: we've got it and it's in our queue.
  • Follow up: you've replied, and it's back with our team.
  • Awaiting your reply: we've replied and need something from you.
  • Closed: resolved. Reply to a closed ticket to reopen it.

Site down?

Call 678-379-9321 as well as opening a Critical ticket.

Keep your email current

Ticket replies go to the email address on your account. You can update it, your name, or your password under Email & password in the support area.

Not a client yet?

Support tickets are for clients. To learn about ongoing care, see Website Care & Hosting, or contact us at 678-379-9321 or This email address is being protected from spambots. You need JavaScript enabled to view it..

How to Install and Update WordPress Plugins Safely

Plugins add features to WordPress, like forms, SEO tools, or a store. They're also the most common reason a WordPress site breaks or gets hacked. A little care up front goes a long way. These steps are for WordPress 6.x and later.

Before you install anything

  • Check whether you really need it. Every plugin is more code to update and more that can go wrong.
  • Look at the plugin's page in the WordPress.org directory: when it was last updated, how many active installs it has, which WordPress version it's tested with, and what people say in the support forum.
  • Only download from trusted places: the WordPress.org directory or the developer's own site. Never use "free" copies of paid plugins. They often contain malware.
  • Back up first. See Website Backups: What to Back Up, How Often, and How Restores Work.

Install a plugin from the directory

  1. Log in at yoursite.com/wp-admin.
  2. Go to Plugins > Add Plugin.
  3. Search for the plugin by name.
  4. Click Install Now, then Activate.
  5. Look for the plugin's settings. They're usually in the left menu or under Settings.

Install a plugin from a zip file

Paid plugins usually come as a zip file you download from the developer's site.

  1. Go to Plugins > Add Plugin.
  2. Click Upload Plugin at the top.
  3. Choose the zip file and click Install Now.
  4. Click Activate Plugin.
  5. If it's a paid plugin, enter your license key in its settings so it can get updates.

Update plugins

  1. Back up your site.
  2. Go to Dashboard > Updates, or Plugins > Installed Plugins and look for update notices.
  3. Read the changelog for big updates (look for View details).
  4. Update a few plugins at a time, not everything at once. That way, if something breaks, you know what caused it.
  5. Check your site after each round: the home page, forms, checkout if you have one, and anything the plugin does.

Rather not deal with plugin updates yourself? We can handle them on demand at reasonable hourly rates, so you only pay for what you need.

For more on the whole process, see How to Update WordPress Safely (Back Up First).

Should you turn on auto-updates?

On Plugins > Installed Plugins, each plugin has an Enable auto-updates link. Once it's on, the column shows Auto-updates enabled, and you can turn it off again from the same spot. (There's also a Manage auto-updates link.) Auto-updates are handy for small, well-maintained plugins and they close security holes fast. For plugins your site really depends on, like a store or a page builder, many people prefer to update by hand so they can test right away. Whatever you choose, have backups running.

Deactivate or delete plugins you don't use

  1. Go to Plugins > Installed Plugins.
  2. Click Deactivate under the plugin.
  3. Click Delete to remove it.

A deactivated plugin is still on your server, so delete anything you're not using. Some plugins leave settings in the database after you delete them. Check the plugin's docs if you want a clean removal.

If a plugin update breaks your site

  • If you can still log in, deactivate the plugin you just updated.
  • If you can't log in, your web team or host can turn it off by renaming its folder in wp-content/plugins.
  • Restore your backup if the site is down and you can't fix it quickly.
  • Open a ticket if you're a client. See How to Get Support From 3by400.

Related

Prefer we handle it?

If you'd rather spend your time running your business, our boutique hosting, available to our clients, including sites moved over from another host, takes a proactive approach to security and monitoring, with nightly backups, 24/7 outage monitoring, and ongoing core CMS updates.

How to Restore a WordPress Site From a Backup

Using Joomla instead? See How to Restore a Joomla Site From a Backup.

WordPress doesn't include a backup and restore tool of its own. Restores are done with a backup plugin or through your host. Here's how the process works.

If your site was hacked, don't restore yet. Read My Website Was Hacked: What to Do Right Now first, or the problem can come right back.

Before you restore

  • Pick the right backup. Choose one from before the problem started. Check the date.
  • Back up the current site too, even if it's broken. You may need something from it.
  • Note recent changes. Anything added after the backup date, like new posts, orders, comments, or form entries, will be lost and may need to be re-entered.
  • Restore to a staging copy first if you can. Many hosts offer staging sites.

Option 1: your backup plugin

  1. Log in at yoursite.com/wp-admin.
  2. Open your backup plugin's screen and find the list of backups.
  3. Choose the backup and select Restore.
  4. Choose what to restore: usually the database, plugins, themes, uploads, and other files. For a full restore, choose everything.
  5. Wait for it to finish without closing the browser.

If you can't log in to WordPress, some backup plugins and hosts let you restore without it. Otherwise, a restore may need server access.

Option 2: your host

Many hosts keep their own backups and can restore them from the control panel or on request. Check whether it restores files, the database, or both. You need both for WordPress.

After restoring

  1. Log in and check that the admin works.
  2. Clear any caching (your caching plugin or host).
  3. Visit key pages, test forms, and check logins.
  4. Go to Dashboard > Updates and apply any updates the backup is missing. See How to Update WordPress Safely (Back Up First).
  5. Re-save permalinks at Settings > Permalinks if pages show 404 errors.
  6. Re-enter any content added since the backup.

When to call us

  • You can't log in and don't have server access
  • You're not sure which backup to use
  • The site was hacked
  • Something still isn't right after restoring

If you're on our boutique hosting, which is available to our clients, including sites moved over from another host, your site has nightly backups kept for one week. Contact us about restoring from one. We can do restores on demand at hourly rates. See Website Backups: What to Back Up, How Often, and How Restores Work.

Prefer we handle it?

If you'd rather spend your time running your business, our boutique hosting takes a proactive approach to security and monitoring, with nightly backups, 24/7 outage monitoring, and ongoing core CMS updates.

How to Update WordPress Safely (Back Up First)

Using Joomla instead? See How to Update Joomla Safely (Back Up First).

Updates fix security holes and bugs, so keeping WordPress current is one of the best things you can do for your site. Here's how to do it without surprises.

1. Back up first

Take a full backup of your files and database, and make sure you know how to restore it. Your backup plugin or host can do this. See Website Backups: What to Back Up, How Often, and How Restores Work.

If your host offers a staging (test) site, try the updates there first.

2. See what needs updating

  1. Log in at yoursite.com/wp-admin.
  2. Go to Dashboard > Updates. This lists updates for WordPress, plugins, themes, and translations.

Before a big update, check each plugin's details for whether it's been tested with your version of WordPress.

3. Update in this order

  1. WordPress core: on Dashboard > Updates, click Update to version x.x (or Update Now). Minor and security updates often install automatically in the background.
  2. Plugins: on Dashboard > Updates, tick the plugins and click Update Plugins. Or go to Plugins > Installed Plugins and click update now under each one. Update a few at a time.
  3. Themes: tick themes on Dashboard > Updates and click Update Themes.

Paid plugins and themes may need an active license to update.

Customized your theme? If someone edited your theme's files directly, updating it will overwrite those changes. Ask your web team first. A child theme protects against this.

4. Test your site

  • Clear any caching (from your caching plugin or host).
  • Visit the home page and key pages.
  • Submit your forms.
  • Check anything that relies on plugins, like stores, galleries, or bookings.
  • Log in and out.

Automatic updates

On Plugins > Installed Plugins, you can Enable auto-updates for each plugin. It saves time, but you won't be watching when an update runs, so make sure backups are running and someone checks the site regularly.

If something breaks

  • Note what you updated and what's broken.
  • Check Tools > Site Health for clues.
  • Restore your backup if the site is down and you can't fix it quickly.
  • If you're a client, open a ticket. See How to Get Support From 3by400.

When to call us

  • Your site has a customized theme or custom code
  • An update is flagged as not tested with your WordPress version
  • Your store or bookings depend on the plugins being updated
  • You don't have a recent backup

Prefer we handle it?

If you'd rather spend your time running your business, our boutique hosting, available to our clients, including sites moved over from another host, takes a proactive approach to security and monitoring, with nightly backups, 24/7 outage monitoring, and ongoing core CMS updates.

Is My Website Slow? Common Causes and Fixes

A slow website frustrates visitors, and they may leave before the page loads. Speed can also affect how your site does in search. Here are the usual causes and what to do about them.

First, measure it

  • Test a few key pages (not just the home page) with a free tool like Google PageSpeed Insights.
  • Test on a phone as well as a computer.
  • Write down the results so you can compare after making changes.

Scores move around between tests, so look at trends and the specific issues the tool lists.

Common causes and fixes

Large images

This is the most common one. Photos straight from a camera or phone are often much bigger than needed.

Fix: resize images to the size they display, use JPEG or WebP for photos, and turn on lazy loading. See images in Joomla or images in WordPress.

Too many add-ons

Every Joomla extension or WordPress plugin can add code, files, and database work to each page.

Fix: remove ones you don't use, and replace heavy ones with lighter options where you can.

No caching

Without caching, the server builds every page from scratch on every visit.

Fix: turn on caching. Joomla has built-in caching under System > Global Configuration > System and a System - Page Cache plugin. WordPress usually relies on your host or a caching plugin. Clear the cache after making changes.

Hosting

Cheap shared hosting can be slow, especially when other sites on the same server are busy.

Fix: look at your host's plan, server location, and PHP version. Upgrading hosting can make a big difference.

Outdated software

Old versions of PHP, Joomla, WordPress, and add-ons are often slower.

Fix: keep everything updated. See Why Updates Matter (and What Boutique Hosting Covers).

Third-party scripts

Chat widgets, social feeds, embedded videos, maps, and tracking codes all load from other servers.

Fix: keep only the ones you need, and load videos and maps only when someone clicks.

Fonts

Several font families or weights add up.

Fix: use fewer fonts and weights, or system fonts.

Database clutter

Old revisions, spam, and leftover data from removed add-ons can slow things down.

Fix: clean up regularly, with a backup first.

When it's not your site

If the whole site is suddenly slow or down, it may be a hosting issue or even a hack. See My Website Was Hacked: What to Do Right Now if you're seeing anything odd.

How 3by400 can help

Our boutique hosting includes server tuning specifically for Joomla and WordPress, plus ongoing core CMS updates.

Start a project

Ready to talk about your website? Start a project or reach us at 678-379-9321 or This email address is being protected from spambots. You need JavaScript enabled to view it.. We're based in Dalton, GA, and work with businesses everywhere.

Joomla 3 Ending, Upgrade to Joomla 4. What you need to know!

What is Joomla?

You may be asking yourself, "What is Joomla?" Joomla is an award winning, free and open source content management system (CMS) for publishing web content. The name Joomla is a phonetic spelling for the Swahili word "Jumla," which means "all together" or "as a whole". Since it's inception in 2005, Joomla has grown to be the second most widely used website platform globally, nearly 2 million active websites. A large community of developers and contributors have worked together to make Joomla flexible, user-friendly, extensible, secure, and robust. Additionally, thousands of "extensions" have been developed by the Joomla community to further enhance the capabilities of the Joomla platform, including extensions developed by 3by400!

What's happening to Joomla 3?

Joomla 3 was original released on September 27, 2012 and continued being improved upon until it's 3.10 LTS (Long Term Support) version release on August 17, 2021. The LTS release marked the point at which Joomla 3 would only continue receiving security updates, no feature improvements or additions. Security updates are intended to keep the version as secure as possible by resolving any vulnerabilities that are found. The LTS version will continue receiving security updates for a period of one year, until August 17, 2023. At that time Joomla 3.x will no longer receive any security resolutions and will quickly become a vulnerability. The Joomla Project continues to work toward advancements in the latest versions of Joomla, and in doing so, must set limits on efforts given to older verisons of Joomla. To see a full list of Joomla versions and end dates visit Joomla Lifecycle (EOL).

If you know your website was built using Joomla but you're unsure of the version in use, visit Joomla's guide containing step-by-step instructions for finding the installed Joomla version.

Will my Joomla 3 website stop working in August?

Even though Joomla 3 will be reaching the end of it's support period in August 2023, your website will not cease operating at that time.What will happen is the Joomla Project will cease releasing any further security patches and bug fixes for Joomla 3. This means in the future there will be issues in Joomla 3 that will no longer be resolved, and most importantly Joomla 3 sites will be exposed to security vulnerabilities with no patches to protect them. This is why it's always best to use the most up-to-date versions of any software, whether that be a CMS for your website or the operating system on your personal laptop.

My site is older than Joomla 3. What should I do?

😬 😳... Now that the initial shock has subsided, consider why you have not upgraded your site before now. Were you unaware that your Joomla site was in need of an upgrade? If that is the case you need a web team! Your web team can keep your site updated for you, or reach out when updates require more collaboration. Or maybe, the site is not of value to your organization? If this is the case, consider taking down the website rather than leaving website visitors open to security vulerabilities. Maybe you were not aware of the implications of an insecure website? Whatever the reason, an outdated website puts you and others at risk of cyber security attacks, phishing, fraud and identity theft. Take action to secure your website and take care of you and your site visitors.

Will Joomla 4 be different from Joomla 3?

A Joomla upgrade comes with more opportunity than just the prospect of avoiding being hacked.Joomla 4 is also packed with some amazing new features to make website administration a breeze. Performance, user-interface design, collaboration features, (and the list goes on) all see large improvements in Joomla 4! For an exhaustive list and description of new features visit the Joomla 4 landing page.

When should I upgrade to Joomla 4?

Is "yesterday" an acceptable answer? All joking aside, if you have not started planning for a Joomla 4 upgrade, start now! It's best to have your Joomla 4 upgrade complete prior to the August 17th deadline. If that's not feasible, completing the upgrade as soon as possible is key to preventing your site from experiencing security issues, security issues that could affect visitors to your website and your organization's reputation.

How do I upgrade to Joomla 4?

In order to upgrade to Joomla 4, you'll need to do some prep work first.

You'll want to first verify that your current hosting server meets the minimum system requirements for Joomla 4. Keep in mind that your current server might be specifically configured for your Joomla 3 site in order to keep older extensions functional. If this is the case, you may need to use a different server to place a copy of your site and perform the Joomla 4 upgrade there.

Secondly, perform an audit of all extensions installed on your Joomla 3 site. Verify that a Joomla 4 compatible version of each extension is available. This includes templates as well. If a Joomla 4 version is not available find a replacement or consider if the extension is in use. The Joomla 4 Pre-Update check can help during this step. It can be found in the Joomla Update component. In order to see the Pre-Update check you may need to modify your update channel to be "Joomla Next".

Next, create a backup copy of your website to use for the upgrade. You never want to perform the upgrade on your live website! If your current hosting is compatible with Joomla 4 the backup copy can be placed on your existing hosting. If it's not compatible, place the backup copy on a server that will support Joomla 4.

On the backup copy of the site uninstall any extensions you determined do not have a Joomla 4 version available. With the remainder of the extensions, unpublish all of them. Also, set the default site and admin templates to Joomla core templates.

Next, visit the Joomla update component and follow the prompts to install the latest Joomla 4.x upgrade.

If successful, the upgrade should result in your site's backend now being displayed in the Joomla 4 administrative template.

Next, we recommend visiting your extensions list, filtering by the disabled extensions, and one-by-one, install the Joomla 4 compatible version of each extension and enable the extension if not done so automatically by the extension update. If an extension is already at it's latest version, enable the extension and verify that your site is still loading without error. Also, attempt to enable your intended template and verify it's working. Taking this one-by-one approach will make it easy for you to identify any extension that is causing an issue and resolve or replace it.

That sounds overwhelming. Can 3by400 perform my Joomla site upgrade?

Absolutely! We perform website upgrades every day and will be happy to do the same for you! If you're new to the 3by400 family, reach out to us via our contact form. Existing clients, if you've not already done so, please reach out and allow us to schedule your Joomla upgrade during a convenient time for you!

My Website Was Hacked: What to Do Right Now

Finding out your website's been hacked is stressful. Take a breath. These steps will help you limit the damage and get back on track.

Existing 3by400 client? Call us at 678-379-9321 and open a Critical ticket. See How to Get Support From 3by400.

Signs your site may be hacked

  • Visitors get sent to spam, gambling, or scam sites
  • Pages you didn't create, often in other languages
  • Search results showing odd titles or descriptions for your site
  • A browser or Google warning that the site is unsafe
  • Admin users you don't recognize
  • Your host suspends the site or sends a warning
  • Emails from your domain bouncing or being marked as spam

What to do right now

  1. Don't panic-delete things. Deleting files or the whole site can destroy what's needed to find out how the attacker got in.
  2. Contact your host. They may see the problem from the server side and can sometimes put the site in maintenance mode or restore a backup.
  3. Change passwords from a clean device. Start with your hosting account, then site admin accounts, FTP/SFTP, the database, and email. Use strong, unique passwords and turn on two-factor authentication where you can.
  4. Check admin users. Remove any accounts you don't recognize.
  5. Find your most recent clean backup. Note its date. Don't restore it yet unless you know when the hack started, or you may restore the problem too.
  6. Write down what you see. Screenshots, URLs, and when you first noticed help whoever cleans up the site.

What to avoid

  • Don't just restore a backup and move on. If the hole isn't closed, the attacker can come back.
  • Don't install a pile of security add-ons at once. They can conflict and won't remove what's already there.
  • Don't ignore it. Hacked sites can be flagged by search engines and browsers, which hurts traffic and trust.

Getting the site clean

A proper cleanup usually means:

  1. Finding and removing malicious files, code, and database entries
  2. Finding how they got in, often an outdated add-on, a weak password, or an old copy of the site left on the server
  3. Updating core and all add-ons, and removing ones you don't use
  4. Resetting all passwords and security keys
  5. Asking for a review if Google flagged the site (through Google Search Console)
  6. Watching the site for a while to make sure it stays clean

Preventing it next time

  • Keep core and add-ons up to date
  • Remove add-ons and old site copies you don't use
  • Use strong passwords and two-factor authentication
  • Keep regular, tested backups stored off the server
  • Choose a host that takes security seriously

How 3by400 can help

We clean up hacked Joomla and WordPress sites and keep them updated, backed up, and monitored afterward. See Website Care & Hosting.

Start a project

Ready to talk about your website? Start a project or reach us at 678-379-9321 or This email address is being protected from spambots. You need JavaScript enabled to view it.. We're based in Dalton, GA, and work with businesses everywhere.